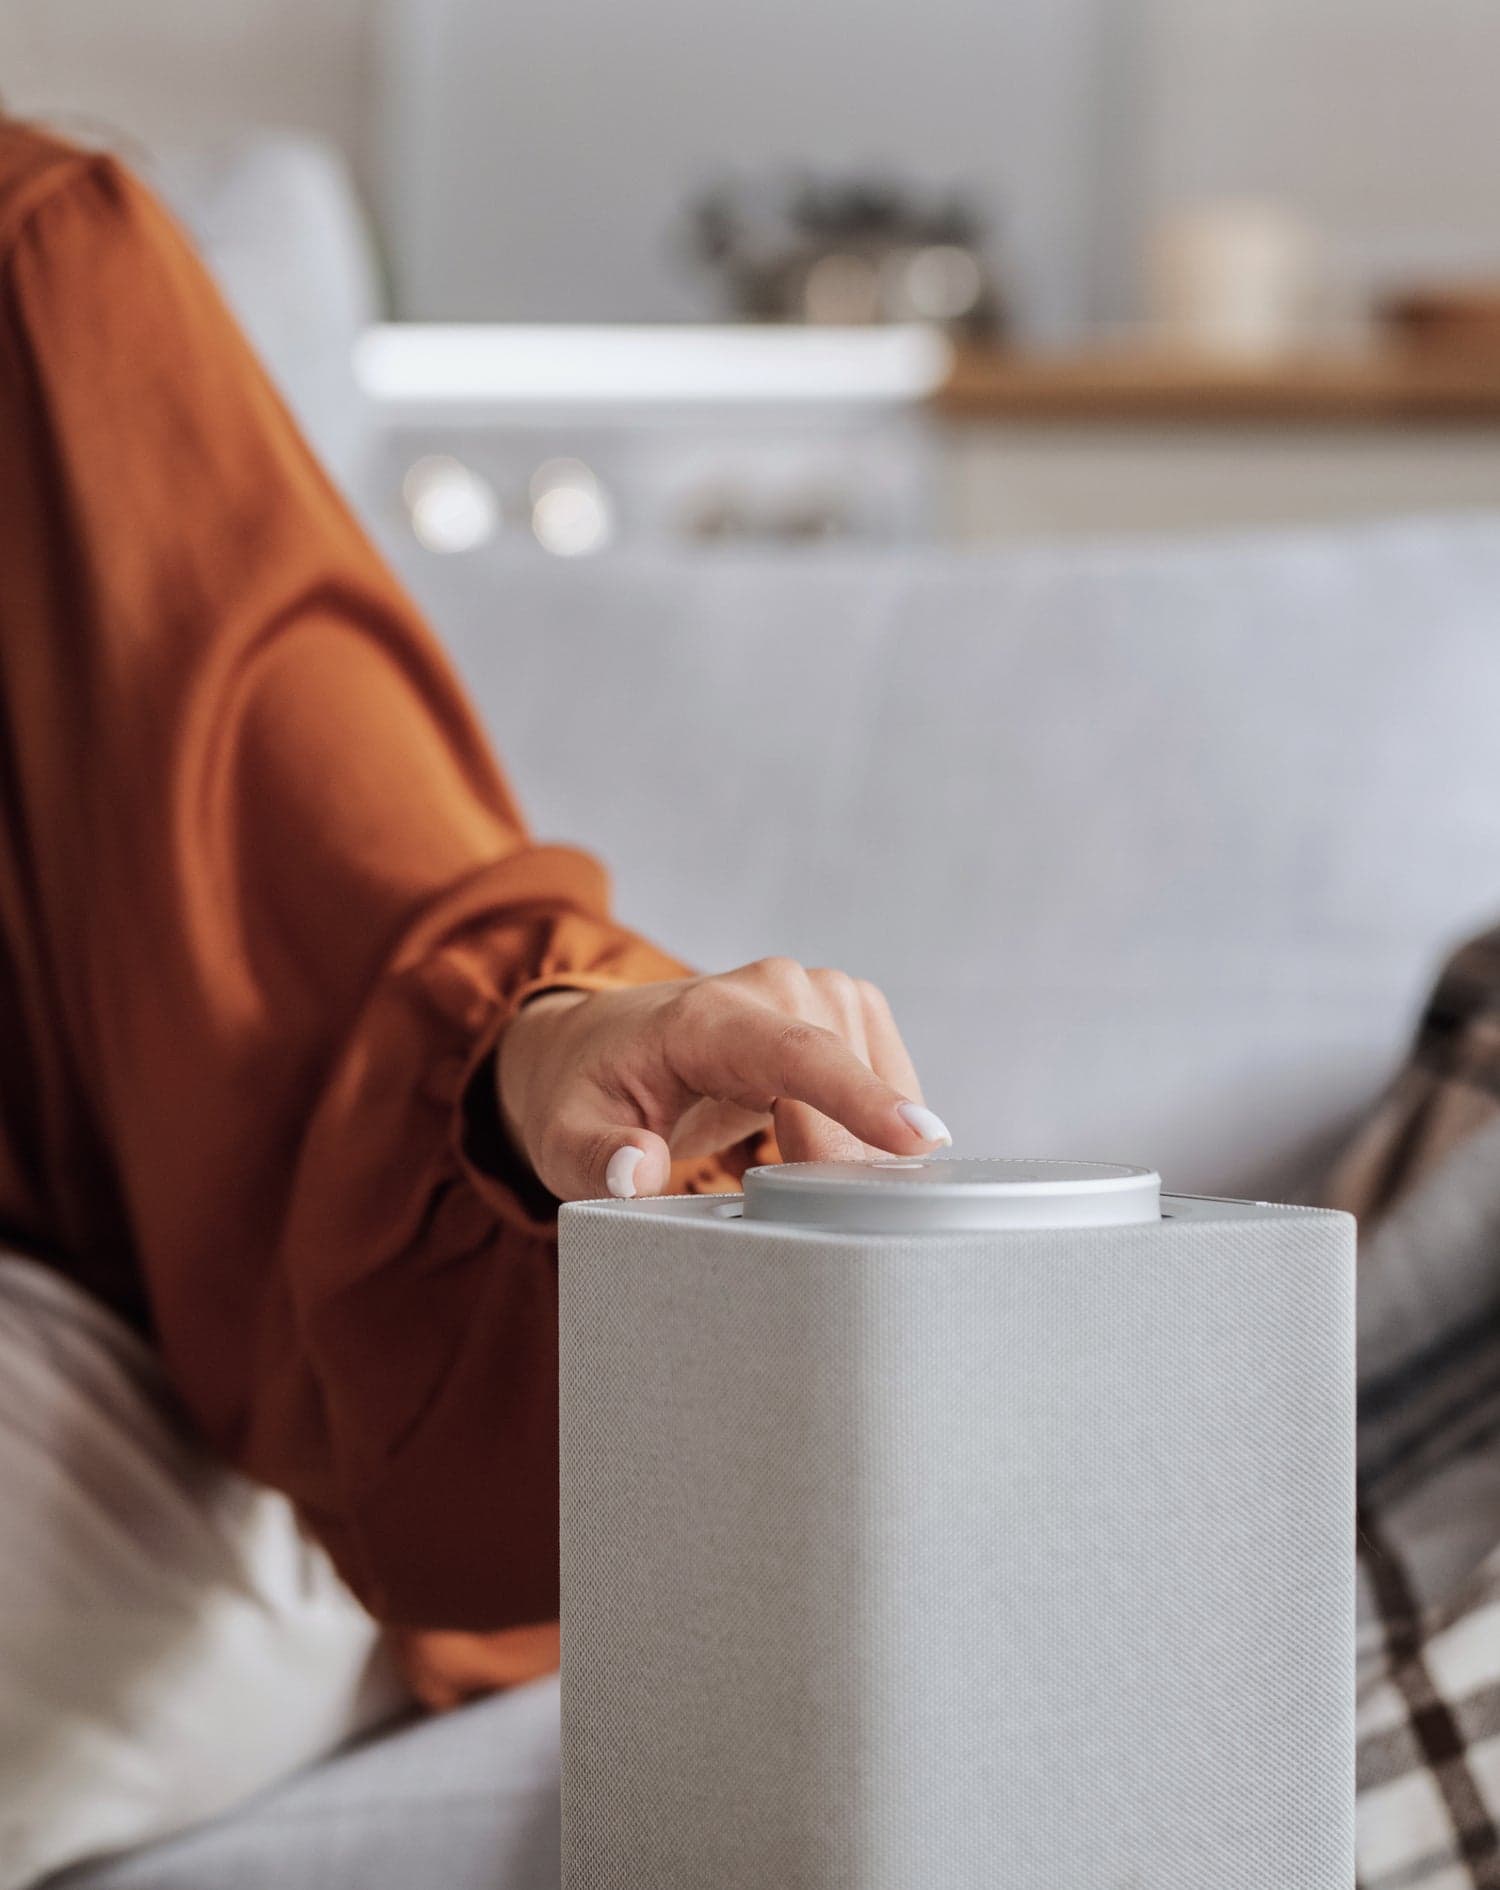
Quick question, and no looking: what is on your clipboard this second? If you pasted right now, into this page, what would come out? A password? A two-factor code you copied to enter somewhere? A crypto wallet address? Your home address? A private message you meant to forward? A file?
Most people genuinely do not know, and that uncertainty is the whole problem. Think about the most sensitive thing you have ever copied, because at some point you have copied nearly all of it, and it all passed through the same small, invisible, shared surface: the clipboard. It holds your single most sensitive item at a time, in plain text, and it is far more exposed than almost anyone realizes.
Anything can read it
The clipboard is a shared resource, and for most of computing history any app could quietly read whatever was on it, no permission, no notice. This is not theoretical. In 2020, researchers caught dozens of major apps, including some of the most popular in the world, silently reading users’ clipboards in the background. That scandal is the reason iPhones now flash a little “pasted from” notification and require permission to read another app’s clipboard, and why Android shows a clipboard-access warning and auto-clears the clipboard after a while.
Those are real improvements, but the exposure has not vanished. A shady third-party keyboard sees everything you type and often everything you copy. A background app can grab the contents in the window before the system clears it. And outright malware does not ask politely at all. Whatever you last copied, a password, a login code, a recovery phrase, is sitting there readable, and you probably were not thinking about it.
The clipboard is where crypto quietly gets stolen
The signature clipboard crime is elegant and brutal, and it is worth understanding because it shows how little the attacker actually needs. It is called clipper malware, and here is all it does: it watches your clipboard, waits for you to copy a cryptocurrency wallet address, and silently replaces it with the attacker’s address before you paste. You paste what you think is your friend’s address, hit send, and your money goes to a stranger. Nothing was decrypted. No password was guessed. No wallet file was opened. The malware just edited your clipboard.
It works because crypto addresses are long, ugly strings nobody reads in full, and it is enormous. Across 2025, wallet-compromise attacks including clippers accounted for roughly 713 million dollars in losses, and a single clipper variant reportedly took over half a million on its own. Mobile is the prime target, precisely because typing a wallet address on a phone is miserable, so everyone copy-pastes. And the clever versions have already defeated the obvious defense: instead of a random address, they swap in a lookalike, one whose first and last characters match the address you copied, so the “I’ll just check a few characters” habit sails right past it. If you move crypto, verify the entire address, every time, not a glance at the ends.
You don’t even need malware to get burned
Here is the part that has nothing to do with hackers. You copy a two-factor code and then paste it, into the wrong chat, a search bar, a form that logs it. You copy a password and it lingers on the clipboard until something replaces it, then you paste it somewhere it should never go. You copy a private photo or file and hand it to the wrong app. The clipboard silently holds the last thing you put there, and a single mispaste leaks it in under a second. That is why “what is on my clipboard right now” is a question worth being able to answer, and usually you cannot.
There is even a growing attack that runs the clipboard in reverse. A malicious web page silently copies a command onto your clipboard just by loading, then shows a fake “there was an error, paste this to fix it” prompt, and tricks you into pasting and running the attacker’s code yourself. From the system’s point of view, you typed the command. Which, unknowingly, you did. Never paste-and-run something a page told you to.
How to take the clipboard back
Because the clipboard is a shared surface, the answer is to stop treating it as a free-for-all and start treating it as something you control.
On a hardened phone, apps are sandboxed and clipboard access is both gated and visible, so you can see when something reads it and deny apps that have no business doing so, and automatic clearing shrinks the window of exposure. Beyond that, a few habits matter more than people think. For passwords and secrets, use a password manager’s autofill rather than copy-paste, so your credentials are not laundered through the general clipboard at all. Clear the clipboard after you copy anything sensitive. Verify crypto addresses in full before sending. And be deliberate about which keyboard you trust, since it sees everything.
This is exactly the gap one of our features is built to close. We make the clipboard’s contents controllable, so you decide what lives there, which apps are allowed to read it, and when it gets wiped, instead of leaving an open, readable surface quietly working against you. The clipboard stops being a thing that happens to you and becomes a thing you manage.
The takeaway
The clipboard is the most sensitive thing on your phone that you never think about. It holds your passwords, your codes, your keys, and your private text, one at a time, in the clear, on a surface that other apps can read and that you can leak with a careless paste. It has been quietly responsible for hundreds of millions in stolen crypto and countless smaller, private spills.
It deserves control, not neglect. If you want a phone where your clipboard is yours to command rather than an open door, email hello@spicycorp.com, or book a call. And in the meantime, maybe clear whatever is on your clipboard right now.
SovereignOS is a hardened, de-Googled phone, set up the way we would build one we had to rely on ourselves. One-time price, no subscription, no account required.
See SovereignOSRecent Posts
- Your Phone, Laptop, and TV Are One Profile. Here’s How They Got Linked.
- Your Advertising ID Is a Tracking Number. Here’s How to Actually Kill It.
- Surveillance Capitalism in Plain English (You’re Not the Product, Your Future Is)
- Does iPhone Lockdown Mode Actually Work? (Yes, and Here’s Where It Stops.)
- Your Data Just Leaked. Here’s the First 48 Hours.
Recent Comments
Post Widget
Why Your VPN Isn’t Hiding Your IMEI
Should You Trust Signal?
Social Media Widget
Customer service
Real people, ready to help. Reach our team anytime at hello@spicycorp.com.
Fast Free Shipping
Get free shipping on orders of $150 or more (within the US)
Returns & Exchanges
We offer free returns and exchanges within 30 days of purchase.